How Blockchain Blocks Store Transaction Data: A Deep Dive
You might think a blockchain is just a giant spreadsheet shared among thousands of computers. But if you dig into the code, you’ll find it’s more like a series of sealed, tamper-proof boxes linked together by mathematical fingerprints. The real magic isn’t in the sharing-it’s in how each blockchain block functions as a permanent, cryptographically secured container for transaction data ensures that once information is written, it can’t be quietly edited or deleted without breaking the entire chain.
Why does this matter to you? Whether you’re sending Bitcoin, minting an NFT, or verifying a supply chain record, understanding how data sits inside these blocks explains why fees fluctuate, why transactions sometimes fail, and why security is so robust. Let’s break down the anatomy of a block, how it links to its neighbors, and the trade-offs between storing everything on-chain versus off-chain.
The Anatomy of a Blockchain Block
A blockchain block isn’t a random pile of digital files. It has a strict structure designed for verification and integrity. Think of it as a package with a shipping label (the header) and the actual goods inside (the transactions).
The most critical part is the block header which contains metadata about the block itself, including the hash of the previous block, a timestamp, and a Merkle root. This header is small-typically under 1KB-but it holds the keys to the block’s validity. If you change even one bit of data in the header, the cryptographic hash changes completely due to the avalanche effect, instantly alerting the network that something is wrong.
- Previous Block Hash: A 256-bit string linking this block to the one before it. This creates the "chain."
- Timestamp: Records when the block was mined, accurate to the second.
- Merkle Root: A single hash representing all transactions in the block.
- Nonce: A number miners tweak to solve the proof-of-work puzzle.
Below the header lies the transaction counter and the actual transaction data. In Bitcoin, this section can hold up to 1MB of raw data (or 4MB with SegWit). Ethereum operates differently, using a dynamic "gas limit" instead of a fixed byte size, allowing roughly 30 million units of computational work per block. This flexibility lets Ethereum handle complex smart contracts, whereas Bitcoin focuses on simple value transfers.
The Role of the Merkle Tree
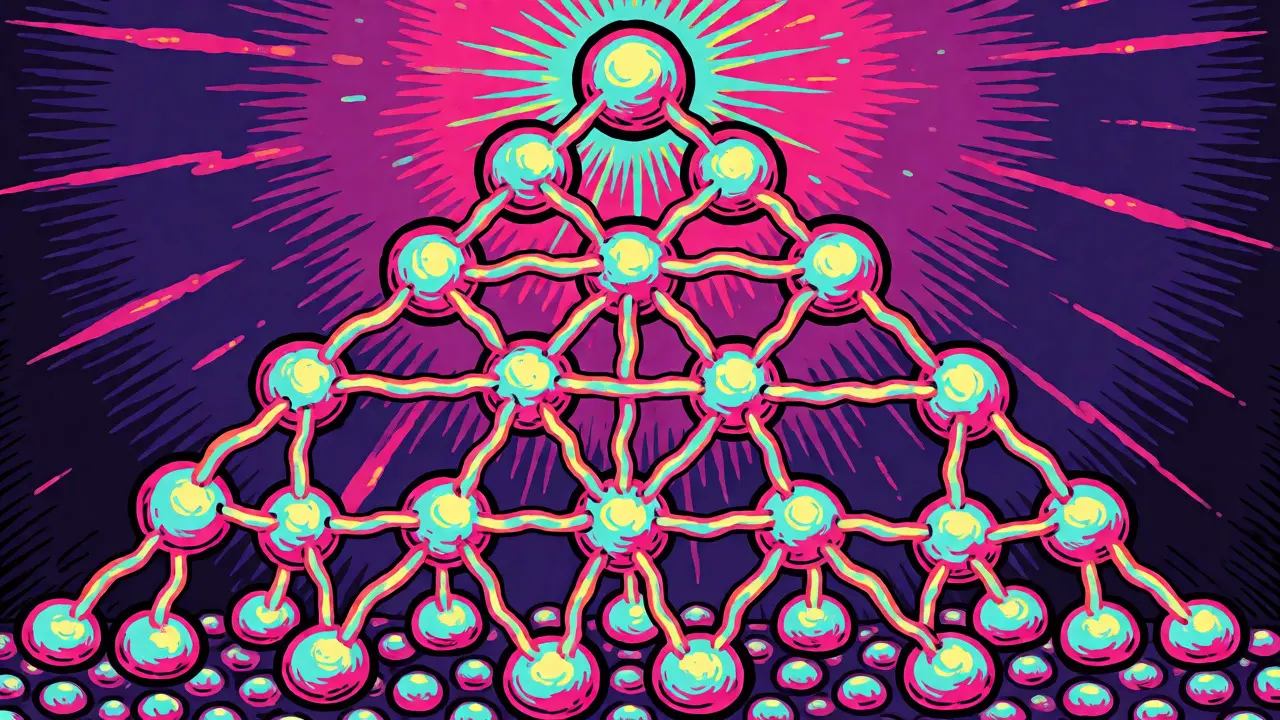
If a block contains 3,000 transactions, how does a node verify just one without downloading the whole block? Enter the Merkle tree a hierarchical data structure invented by Ralph Merkle in 1979 that allows efficient and secure verification of large datasets.
Imagine pairing every two transactions, hashing them together, then pairing those hashes, and repeating until you have one final hash at the top. That top hash is the Merkle Root, stored in the block header. To prove your transaction exists, you don’t need the whole block; you just need a short "path" of sibling hashes. This process, called Simplified Payment Verification (SPV), lets lightweight wallets check balances without syncing terabytes of data.
| Attribute | On-Chain Storage | Off-Chain Storage (e.g., IPFS) |
|---|---|---|
| Security Level | Maximum (protected by network consensus) | Dependent on external protocol security |
| Cost per KB | High ($10+ on Ethereum mainnet) | Low (cents or fractions of a cent) |
| Immutability | Absolute (cannot be deleted) | Conditional (depends on pinning services) |
| Verification Method | Direct read from ledger | Hash comparison against on-chain record |
What Exactly Goes Into a Transaction?
Inside the block, each transaction is a structured object. It’s not just "Alice paid Bob $10." It’s a signed message containing specific fields that the network validates step-by-step.
For Bitcoin, a transaction includes the sender’s address, recipient’s address, the amount in satoshis, and a digital signature proving ownership. Ethereum adds complexity with gas prices, nonce counters to prevent replay attacks, and input data for smart contract execution. These fields are serialized into bytes, hashed, and added to the Merkle tree. If any field is altered-say, changing the recipient-the signature becomes invalid, and the node rejects the transaction.
This granularity is why errors are costly. Once a transaction is included in a block and confirmed, correcting a mistake often requires a new "counter-transaction," which costs additional fees and time. You can’t just hit "undo."
Fiona C
October 25, 2026 AT 20:32Oh, please. The "tamper-proof" narrative is just marketing fluff for people who don't understand distributed systems consensus mechanisms. You're conflating immutability with correctness. Just because a hash chain doesn't break doesn't mean the data inside isn't garbage or manipulated by sybil attacks at the mempool level. This article reads like it was written for someone who thinks SHA-256 is magic rather than a deterministic function with known collision probabilities. It's intellectually lazy to ignore the economic incentives that actually secure the network versus the cryptographic primitives themselves.
mike blogger
October 27, 2026 AT 00:05Great breakdown! Really helpful for beginners.
The Merkle tree explanation is spot on. Keep up the good work!
Tiffany Dickens
October 27, 2026 AT 03:51I appreciate the balanced perspective here. It is crucial to remember that while the structure provides integrity, the human element of key management remains the most vulnerable point in the ecosystem. We should approach these technologies with cautious optimism rather than blind faith.
Michael Houghton
October 28, 2026 AT 03:56It is frankly embarrassing that we are still explaining basic block headers in this manner. The distinction between Bitcoin's UTXO model and Ethereum's account-based state machine is glossed over so heavily that it borders on misinformation. Anyone worth their salt knows that the "gas limit" is not merely about computational work but about resource metering against DoS vectors. This superficial treatment does a disservice to serious developers trying to grasp the architectural nuances. One expects more rigor from technical deep dives in this day and age.
Justin Lemanski
October 28, 2026 AT 13:20wait wait wait
you said merkle root is in header? technically yes but its derived from txs below. also "avalanche effect" is kinda misused here usually refers to symmetric ciphers mostly though sha256 has diffusion properties too. whatever. nice post i guess if ur new to crypto lol
Dawn Askew
October 29, 2026 AT 00:33Straight up nonsense. 🙄
You're telling me I can't edit my own database? Obviously. But comparing blockchain to a "sealed box" ignores the fact that off-chain storage (like IPFS) is where all the actual heavy lifting happens for NFTs anyway. So really, you're just storing a pointer to a file that might disappear tomorrow. That's not "permanent," that's a broken link waiting to happen. Don't drink the Kool-Aid, folks. 🚫
Chukwunanu Sunday
October 29, 2026 AT 03:01chill vibes only 😎
good read man. helps me understand why my tx fees spike when everyone is minting stuff. thanks for sharing 🙏
Wayne Smith
October 29, 2026 AT 05:35Wow. Just... wow. 🙌
We're talking about "mathematical fingerprints" now? Are we five?? And the bit about SPV being efficient? Please. Try running an SPV wallet during a congestion spike and tell me it feels "efficient." It feels like lagging behind reality. But sure, keep peddling the dream that your lightweight client is somehow "secure" without full validation. It's adorable, really. 💅
Lauren Louise
October 29, 2026 AT 13:19Typical American oversimplification. In the UK, we've had robust digital ledger concepts long before Satoshi wandered into the scene. The emphasis on "proof-of-work" as the sole security metric is archaic; proof-of-stake implementations elsewhere handle finality much more elegantly without burning down forests. This article fails to acknowledge global advancements in consensus algorithms, focusing solely on legacy Bitcoin architecture. It’s parochial at best.
Twana Allen
October 30, 2026 AT 10:21This is so important for moral responsibility!! 😡
If you lose your keys, YOU have no one to blame but yourself. There is no central authority to save you. It forces us to be accountable adults. If you can't manage a string of characters, maybe you shouldn't be handling financial assets. Period. End of story. 🛑
Dylan Rondeau
October 30, 2026 AT 16:43Actually, there is a slight correction needed regarding the SegWit size. While the virtual byte limit is often cited around 4MB, the actual serialized size can vary based on witness data. Also, for those looking to optimize costs, batching transactions is a viable strategy that reduces the per-transaction overhead significantly. Hope this adds some value to the discussion!
Erin Williams
October 31, 2026 AT 15:49Loving the clarity here! 👍
For anyone feeling overwhelmed, start small. Understand the header first, then look at the Merkle tree. You've got this!
Jamie Robb
October 31, 2026 AT 23:39honestly who cares about the internal structure if the ui sucks?
i dont care how secure the box is if i cant open it easily. ux > security for mass adoption imo. stop gatekeeping tech with jargon.
Grace Glandy
November 2, 2026 AT 18:53BOOM! 🔥 This is exactly what the community needs right now!
Breaking down the anatomy makes it feel less like black magic and more like engineering. When you realize it's just linked lists and hashes, the fear disappears. Let's get out there and build something amazing with this knowledge! 🚀
Brian Klidies
November 2, 2026 AT 23:54I think the comparison table is particularly useful for visual learners. It clearly delineates the trade-offs between cost and security, which is often the deciding factor for enterprise adoption. Thank you for providing such a structured overview.
Jack Denter
November 3, 2026 AT 06:31Love this deep dive! 🧠💻
The part about the nonce really clicked for me. It’s wild to think miners are just guessing numbers until they hit the jackpot. ⛏️🎰 Thanks for making complex topics accessible! 🌟
gita wijayanti
November 4, 2026 AT 09:59LISTEN UP!!!
You need to STOP thinking of blocks as static files. They are dynamic containers of VALUE transfer. Every single transaction is a battle for space. If you do not understand the fee market, you will LOSE money. This article explains the mechanics, but you must APPLY this knowledge aggressively. Do not be passive with your transactions. Optimize or die. GO GET THEM!
Sheila Inman
November 5, 2026 AT 18:08Good points on the header size constraints. It really highlights why layer 2 solutions are necessary.
Ryan Hall
November 6, 2026 AT 03:42meh. another crypto hype piece. 🤷♂️
we all know most coins go to zero anyway. waste of time reading about "immutability" when the whole system is fragile. sad. 😔
Rebecca Hazelbaker
November 6, 2026 AT 20:40This exposition is truly magnificent in its clarity! ✨
The way you articulated the Merkle Tree concept-specifically the hierarchical pairing of hashes-was nothing short of breathtaking. It illuminated a concept that has previously remained shrouded in mystery for many of us. The precision of your language regarding the "avalanche effect" was equally impressive, ensuring that even the layperson could grasp the severity of cryptographic alteration. Bravo! 👏